Tag: DFIR Products & Solutions

The First Step to Forensic Readiness: Risk Assessment

The first step in achieving forensic readiness is to do a complete risk-assessment analysis of all your business operations. The main goal is to identify any potential risk and vulnerabilities in your business processes so you can understand and define where digital evidence may be required and may benefit the organization.

IREC v2: 1-Click Virus Total results and more

It has been quite a long time since the last time we updated you with what’s new on Binalyze. The reason for that is it was a very busy period full of new features, updates, and even a new product! Now it is time to share the news with you.

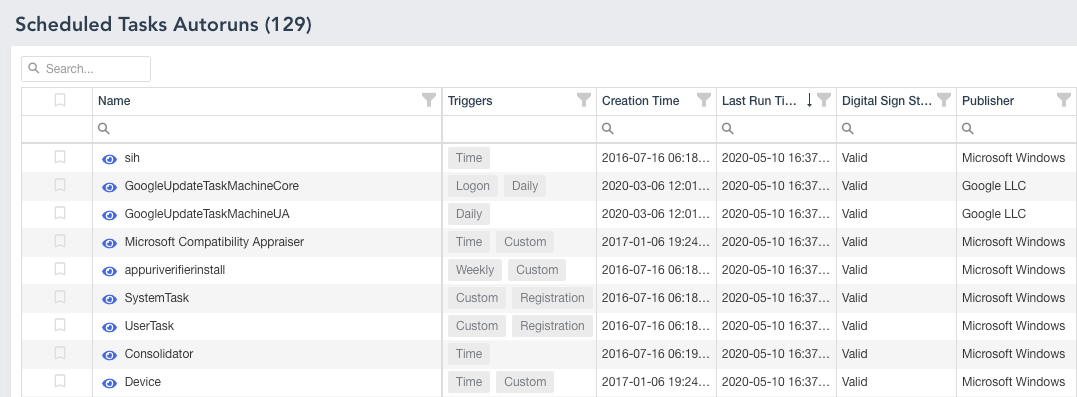
Autoruns

As we all know, investigating a PC is getting harder each and every day due to the increasing complexity of Cyber Attacks. Even though we have designed IREC to be the most complete evidence collector in the market there was still a missing piece: Autostart Locations. As of Windows 10, there are more than 200 registry and file system locations that could be abused by malware and attackers! It means, on a regular PC you will have approximately 1000 entries in total that have the potential of executing malicious code on each system restart. The good news is, IREC v2 lists all of these in an intuitive way with all the information you need such as Digital Signature of the file in question, MAC times for each entry, last write time of the registry key, and the hash of the file!

irec-processes


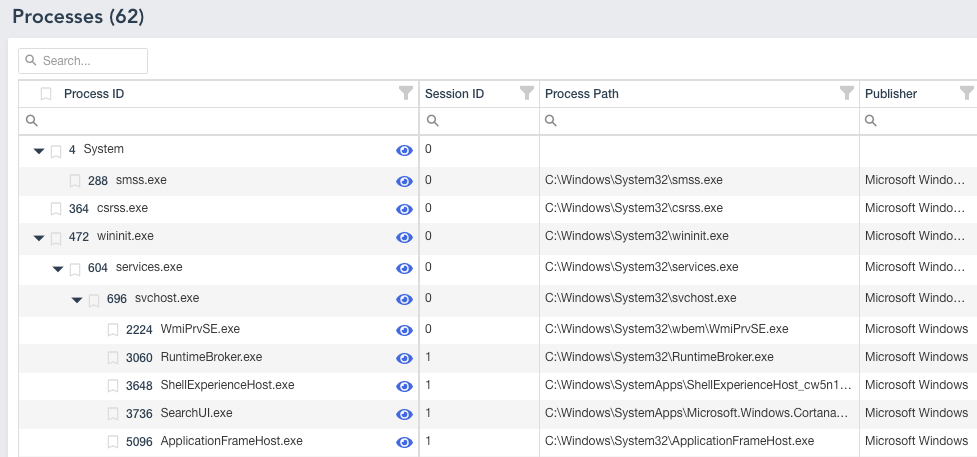
Process Viewer

Version 2 comes with an all-new easy to use process viewer in which you can filter, search, and show the details of each process alongside important information such as TCP Connections, Modules, and other details.

irec-dns-cache


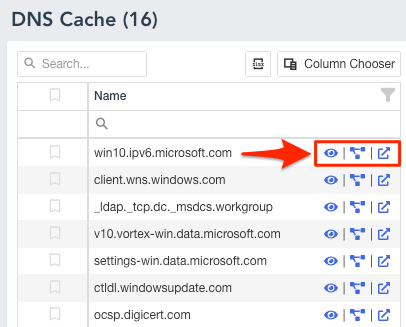
1-Click Virus Total results

The new report lets you view Virus Total results and relations for each URL and IP Address with a single click.

irec-blog


Bookmarking

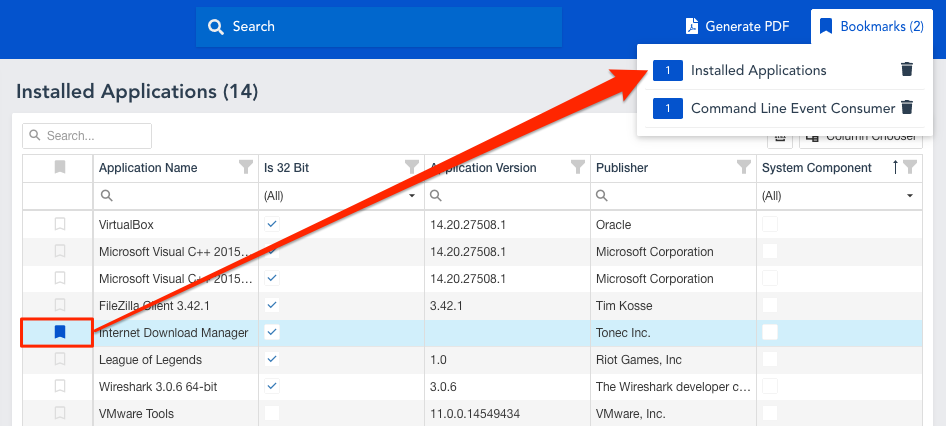
Wouldn’t it be great to bookmark the pieces of evidence either for further investigation or reporting purposes? That’s why we have added an easy bookmarking feature which will persist in the browser’s local storage. So you won’t lose your bookmarks even when you close the browser.

irec-bookmarks


This is just a quick summary of what we have added to the latest version so far. For the full list you can visit IREC page.

SUNBURST Back Door knocking on the World’s Front Door

FireEye has uncovered a malicious campaign that gains access to victims via trojanized updates to Orion, SolarWinds’ IT monitoring and management software.

While the fireworks are only visible to us now, the fuse for this malicious campaign was lit in March 2020. SUNBURST is the product of highly evolved cyber criminals that resulted with significant lateral movement and data theft.

Nationwide Damages

The malicious campaign that compromised just one piece of the SolarWinds IT toolkit potentially gained access to multiple entities nationwide including government agencies, telecommunications companies, top accounting firms and big players from the private sector. Unfortunately, this still only represents a small piece of the extraordinary array of possible SolarWinds’ customers.

SUNBURST Backdoor: ‘update is available, click here to download’

In the spring of 2020 IT staff got a pop up notification from a trusted popular software provider to install a new update and so with one click around 18,000 customers across various government and private organizations downloaded the update and with that the silent game began.

Little did they know that the new update came with a Trojan, secret malicious code, that stayed in their system silently for a couple of weeks, just observing while the victims carried on with their hardworking jobs oblivious to the threat. When the time was just right, SUNBURST sprang into action inside thousands of computer networks in government, technology and telecom organisations across North America, Europe, Asia and the Middle East opening the door for its creator to enter as well. According to BBC the damages are not yet known, but for months the professional cyber criminal team could spy and keep on stealing information of different organisations worldwide.


DFIR Guide

Download our DFIR Guide and learn more how you can elevate your incident response processes.

{{cta(‘b738efd9-03c6-4b79-8e63-1667724d6ddc’,’justifyleft’)}}


SUNBURST: It’s time to take an initiative

Attacks of this nature don’t just affect the infected organisations, they also deal a blow to the entire cyber-security space by undermining trust in our solutions and planting seeds of doubt in users’ minds.

At Binalyze, our core mission is to help our users and the DFIR community to respond faster. As part of this mission we have decided to give support to SUNBURST damaged entities and we hope that this initiative will be supported by other cyber security vendors and professionals.

Today we are releasing a version of Binalyze AIR with the codename SUNBURST that will enable anyone to identify their exposure to the attack and pinpoint their network vulnerability in under an hour.

This version is available FREE OF CHARGE for 15-days and 25,000 endpoints to help all organizations potentially affected by SUNBURST.

Heads up for the DFIR community

To investigate this SUNBURST breach it will take a lot of time, research and financial resources, just when we were getting ready for the Christmas and New Year holidays. Now instead of planning a cosy vacation you have to respond to the biggest breach of the year and plan your DFIR strategies and methods, working hours of overtime trying to manage breach damages.

Binalyze is the fastest evidence collection, triage, and IR investigation platform that now also contains the YARA Rules for SUNBURST thanks to our colleagues at FireEye. We are here to give support to any DFIR community member requesting it that has clients damaged by the hack to help speed up the investigation process and ease your workload.

Over the next few days, we will post videos and blogs sharing DFIR methods and tactics that we believe will be useful to the DFIR community. If you have or had a trojanized version of SolarWinds Orion on your infrastructure, Stroz Friedberg have released this excellent document with advice for a risk-based approach to the situation. Click here for more details.

We are all striving for a safer cyber world and taking our part in this global effort.

Stay safe.

Ransomware Attacks: Plan or Pay

Ransomware is not new but it continues to be one of the biggest challenges for every kind of organization in recent years. There were a total of 308 million ransomware attacks in 2020. This means a 62 percent increase from 2019. At the same time, ransom payments are also increasing. In the first quarter of 2021, the average of ransom payments was over $220,000.

Start triage with already set YARA rules for SUNBURST

3 weeks ago, one of the biggest breaches happened where FireEye uncovered a malicious campaign that gained access to victims via trojanized updates to Orion, SolarWinds’ IT monitoring and management software. Being aware of the nationwide damages this breach will produce, Binalyze released an initiative where we decided to give support to SUNBURST damaged entities by releasing a version of Binalyze AIR with the codename SUNBURST that will enable anyone to identify their exposure to the attack and pinpoint their network vulnerability in under an hour.

This version is FREE of charge for 15-days and 25,000 endpoints.

Binalyze is the fastest evidence collection, triage, and IR investigation platform that now also contains the YARA Rules for SUNBURST thanks to our colleagues at FireEye. In the below lines you will find instructions how to perform a triage with already set YARA rules for SUNBURST in less than an hour.

Now it is time to showcase how easy it is.

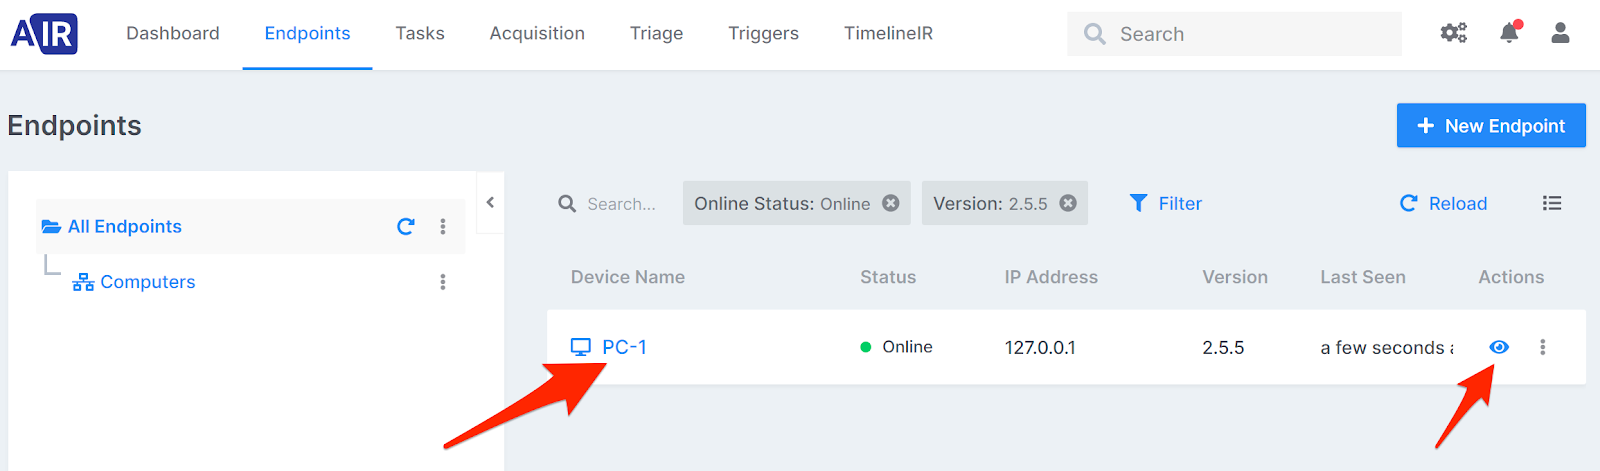
  1. Select an endpoint

    yara-rules-air

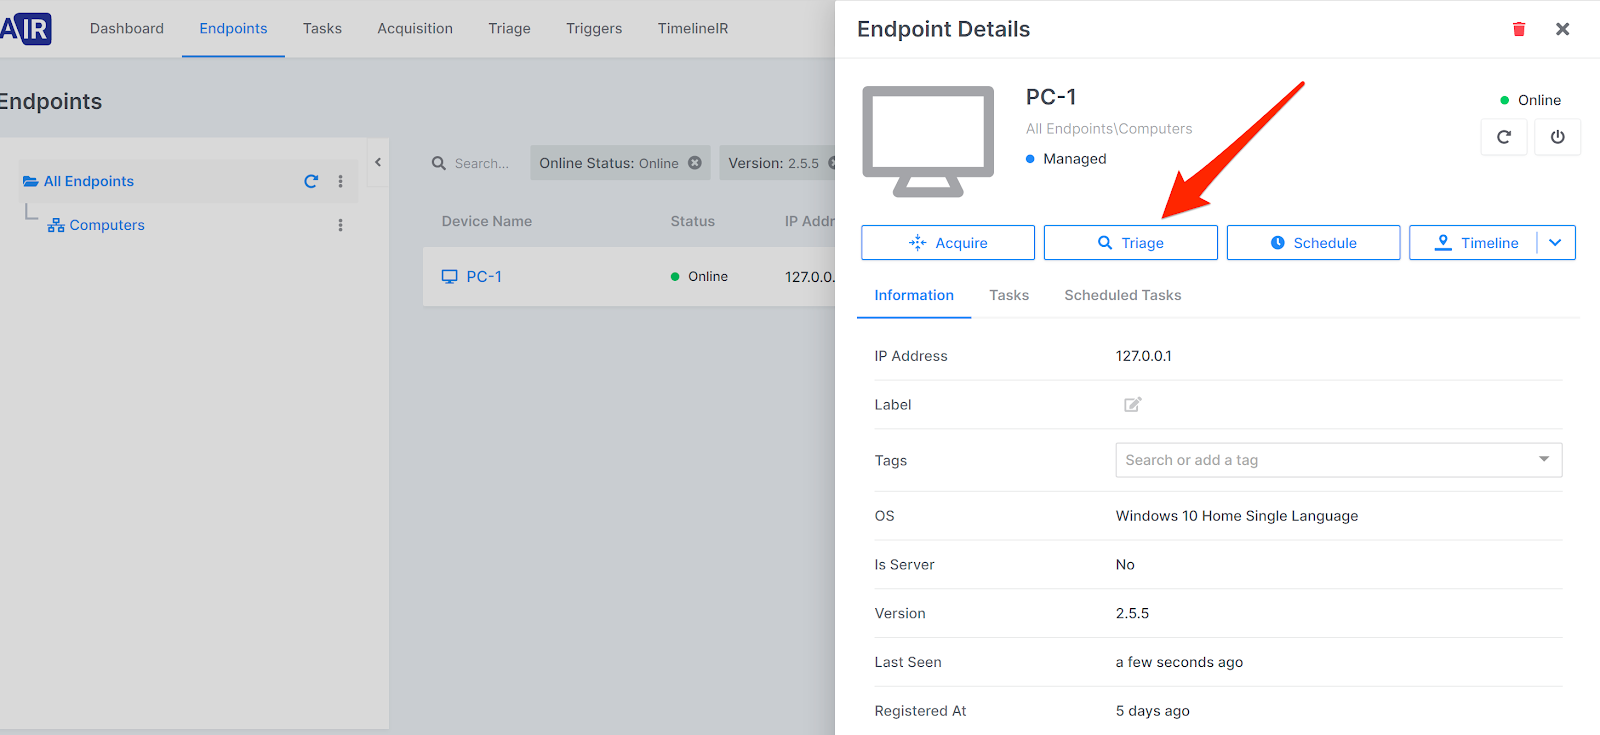
  2. Click on “Triage” button

    sunburst-yara

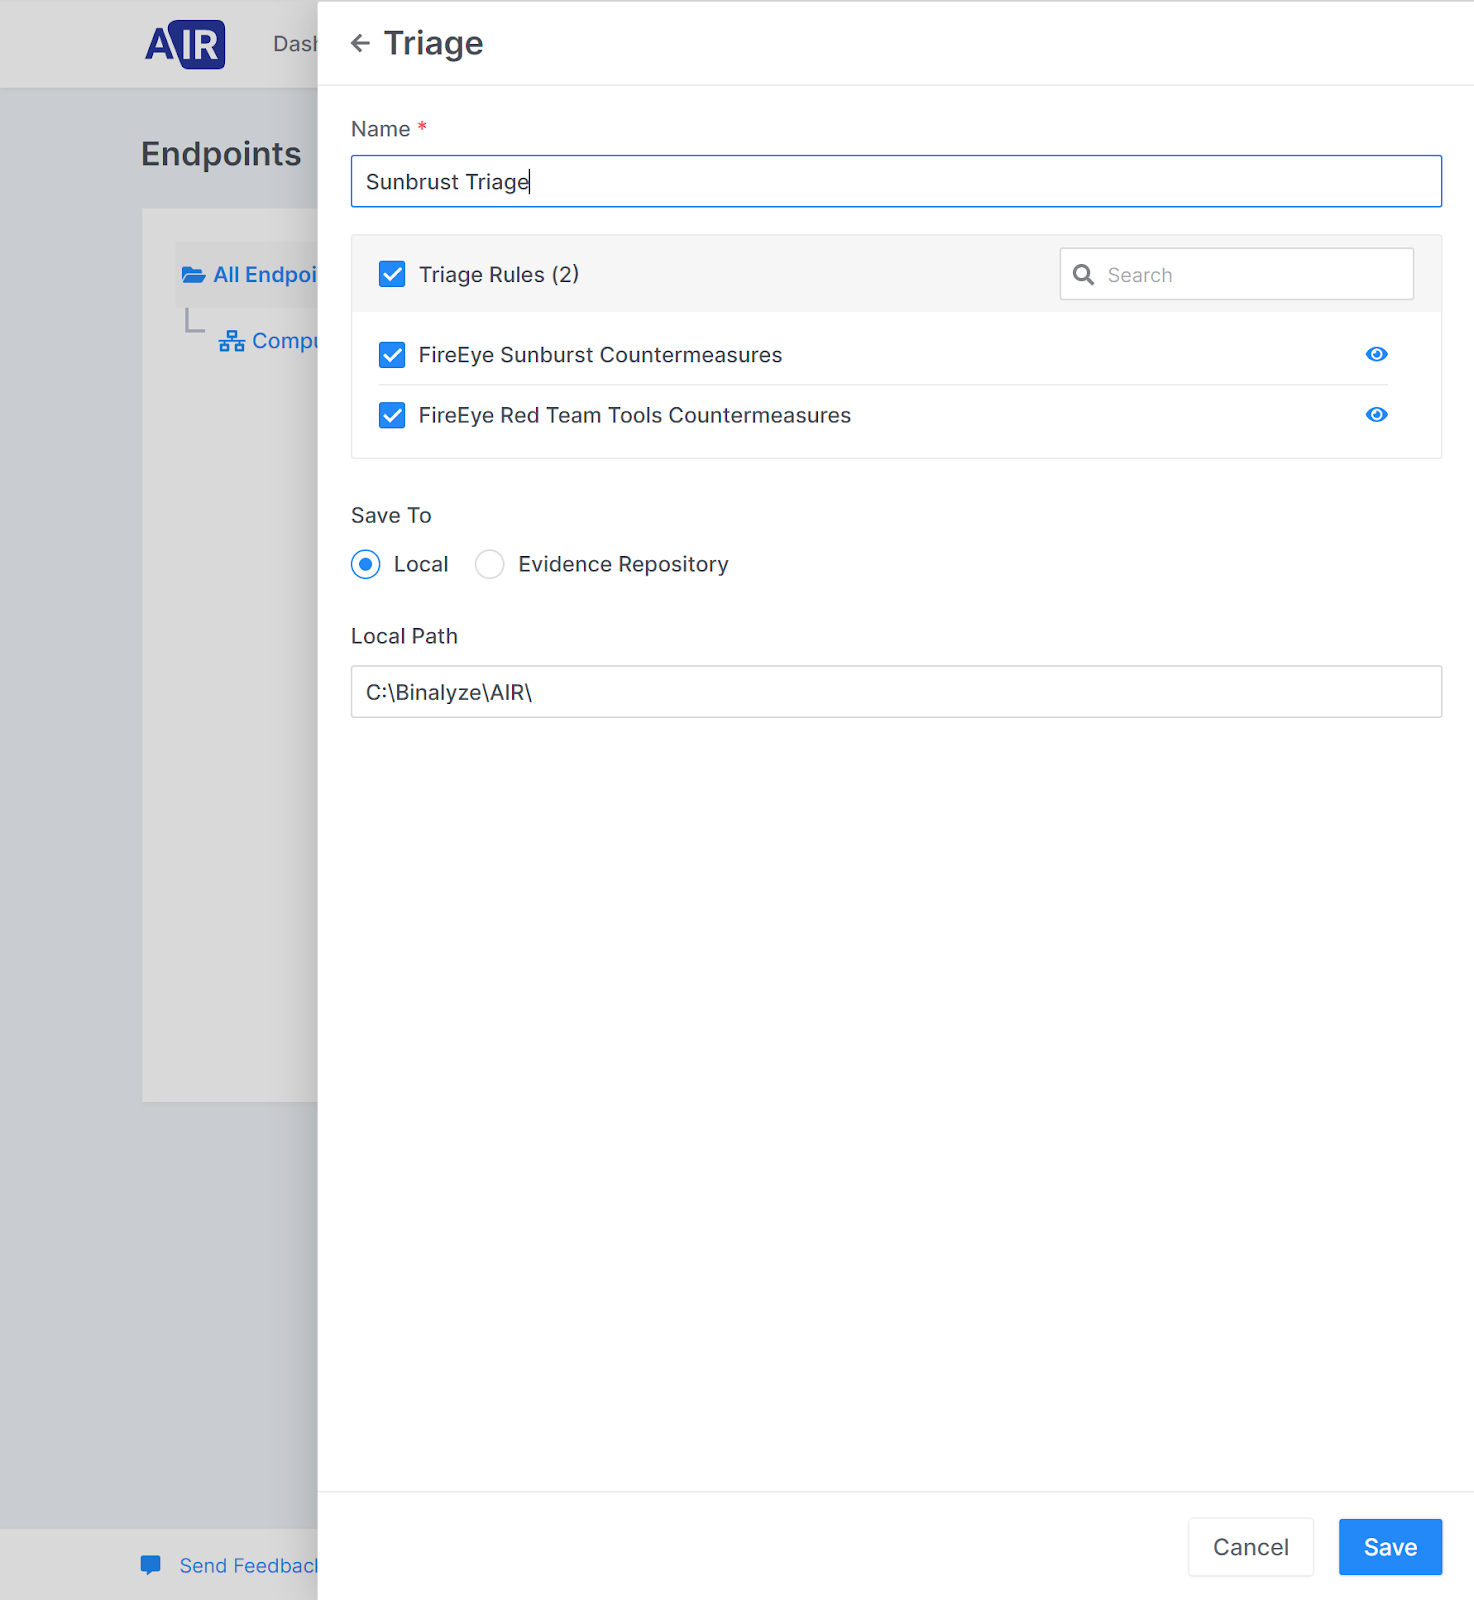
  3. Select both SUNBURST YARA rules and click on “Save”.

    yara-rules-sunburst

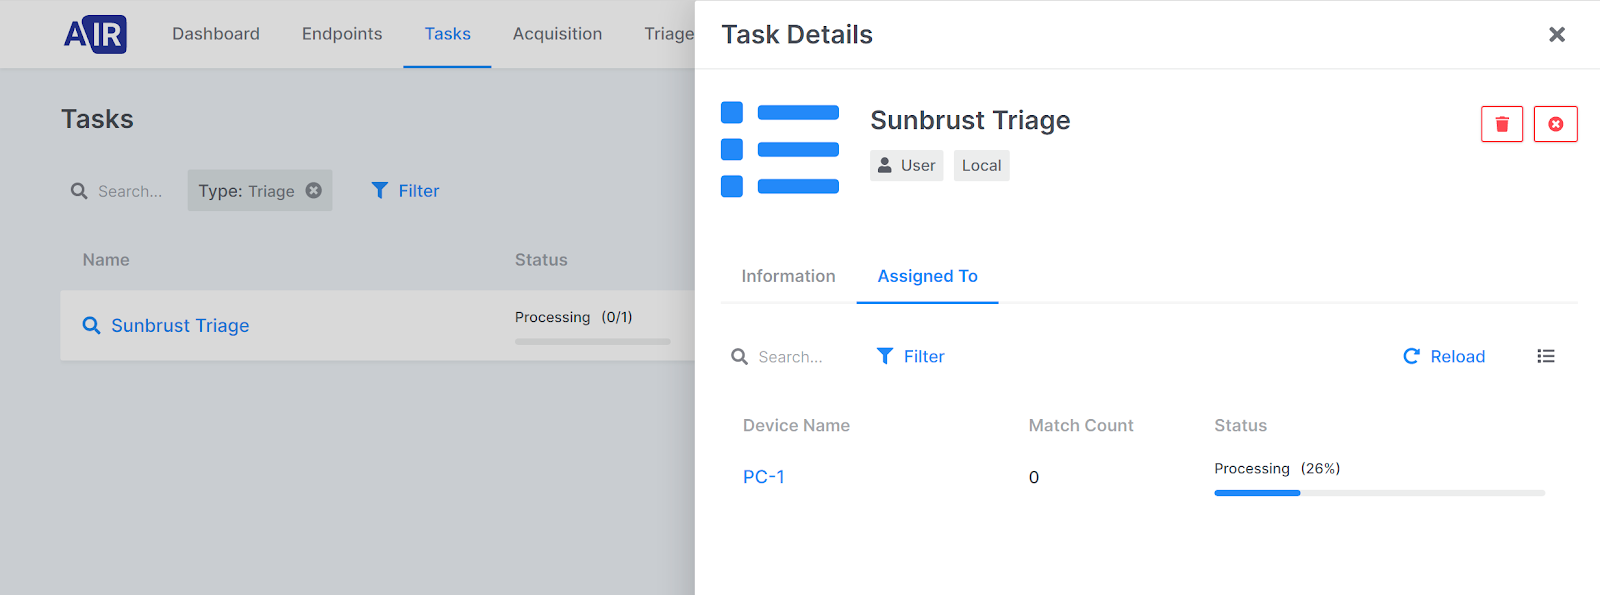
  4. Triage is now in processing.

    yara-sunburst

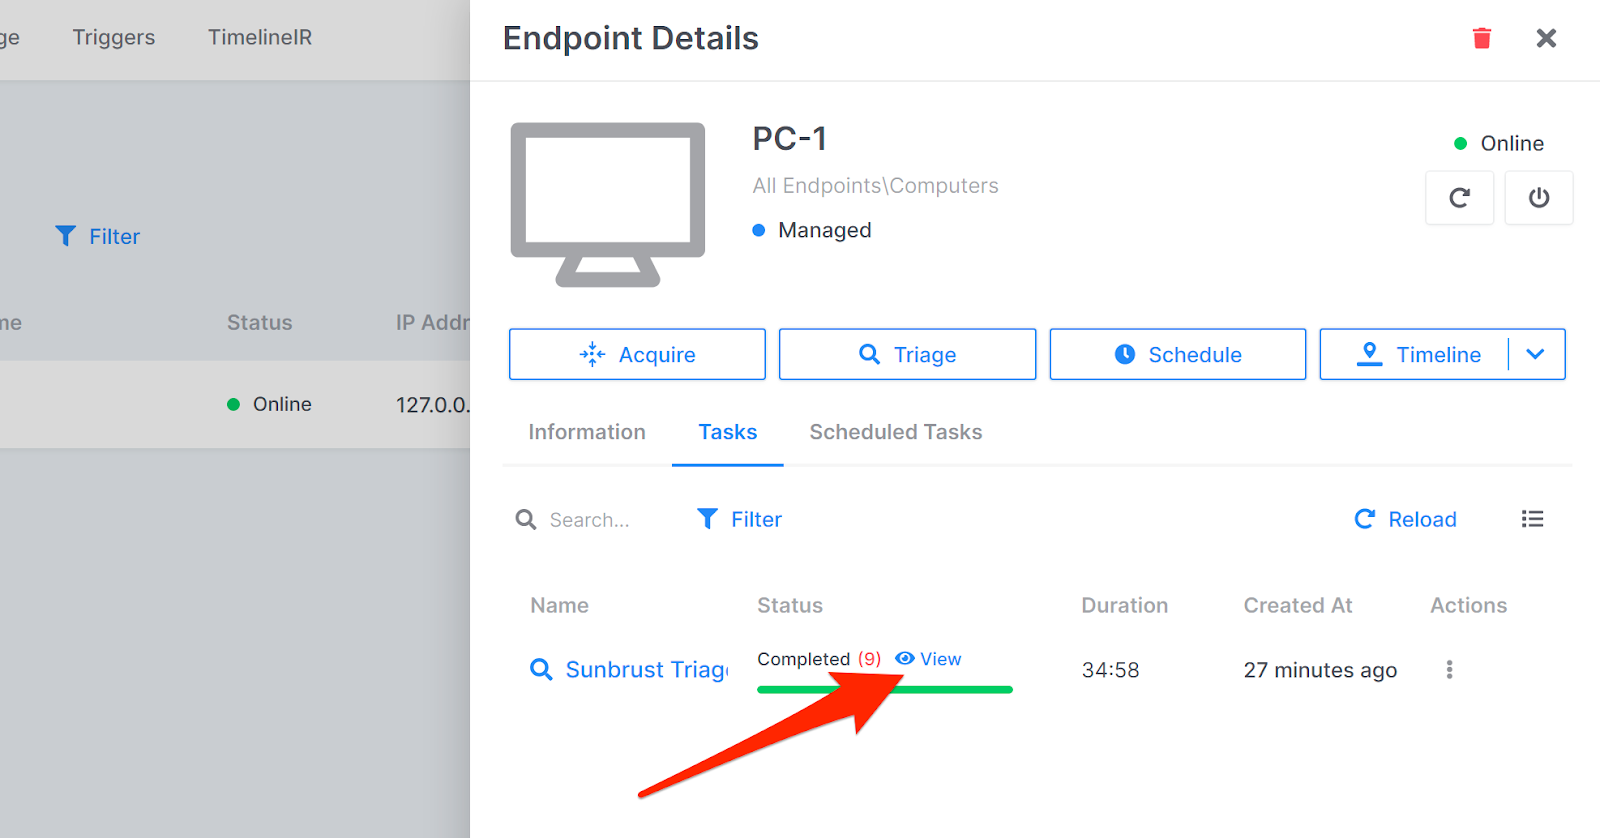
  5. As said it is done in less than an hour or to be exact in 34 minutes.

    yara-rules

  6. To see full view of the investigation results click on “View”.

{{cta(‘cea177d3-11e7-42f2-a4b1-8007f735fad0’)}}